Hey! How about a bug report so I can figure it out? 

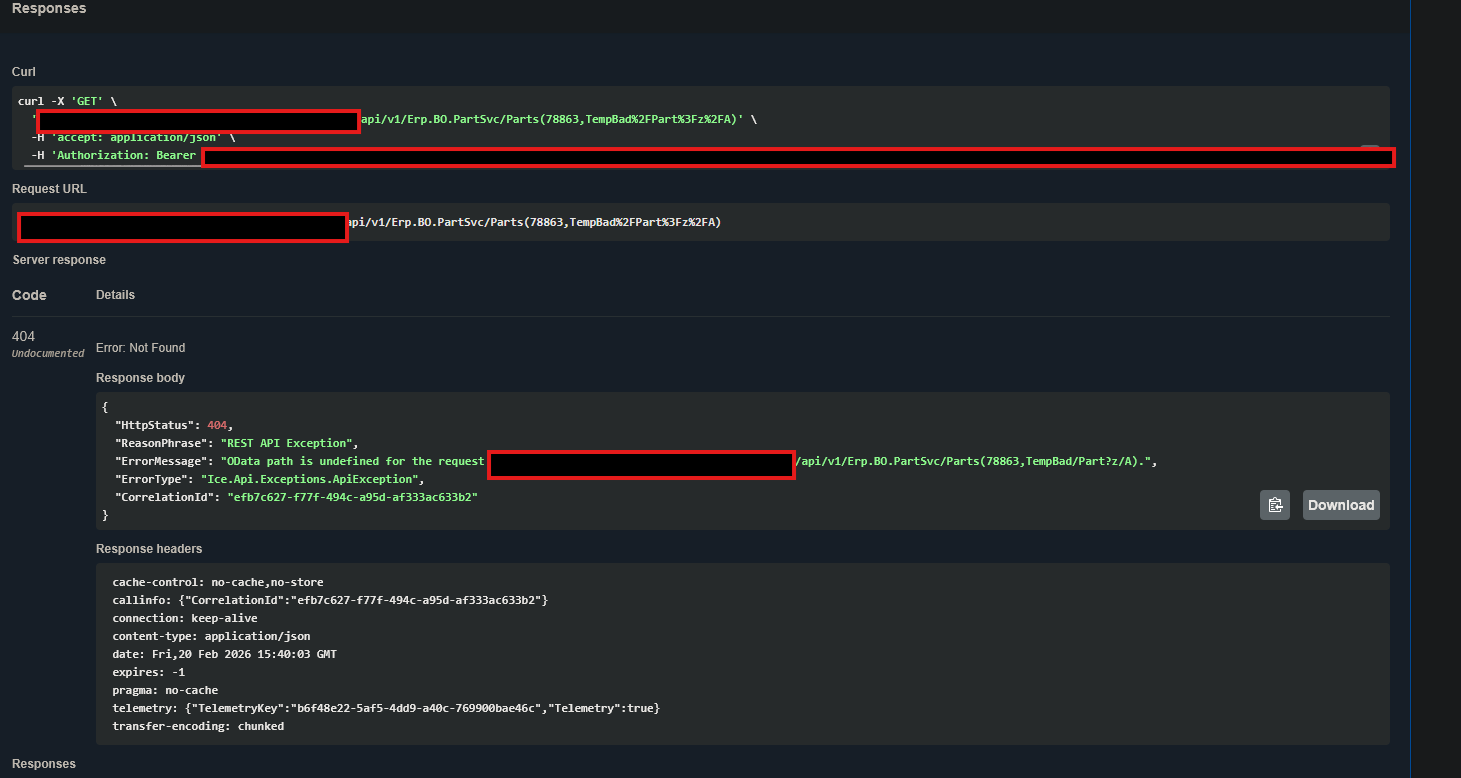
They said last night they’ll be writing up a PRB for development to look at. It’s super easy to replicate - just hit the Erp.BO.PartSvc/Part OData endpoint with a part# that contains a slash. My real curiosity is if this is isolated to us, or if it affects everyone. We’re on 12.1.100.10.
I am surprised if it ever worked. / Usually indicates part of the path in the URL
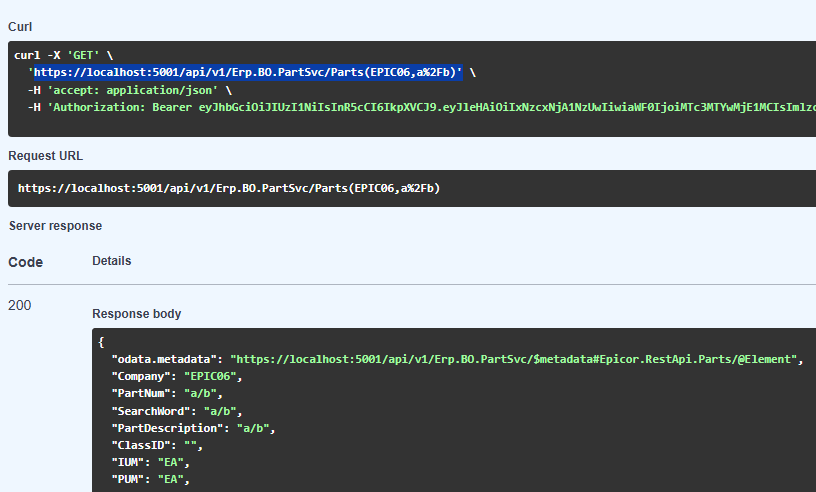
You can see in his screenshots its being escaped as %2F so I wonder if that is really the root of the issue.
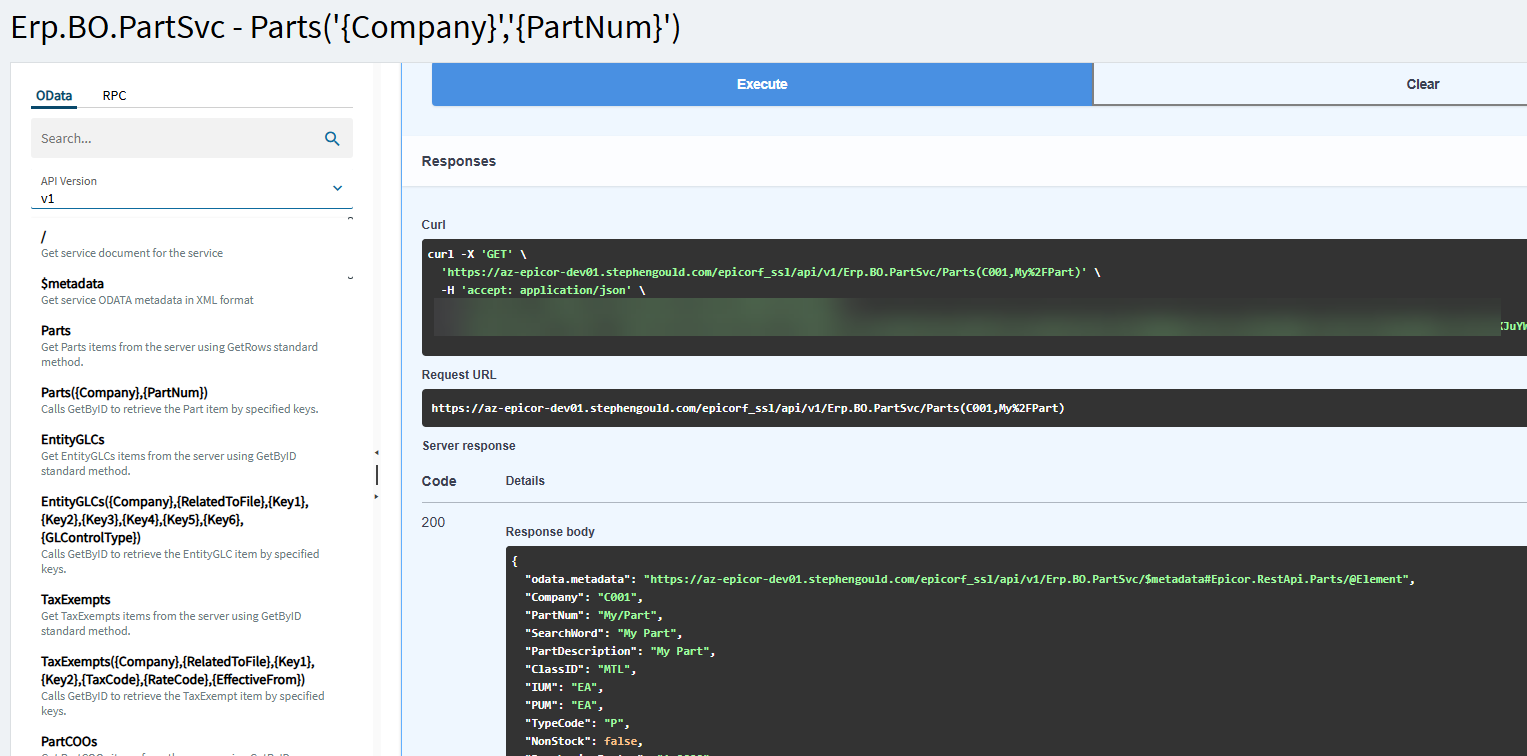
Interesting! Thank you for testing this, Jose. I’m going to update one of our dev instances to .12 and see if this is still happening there.
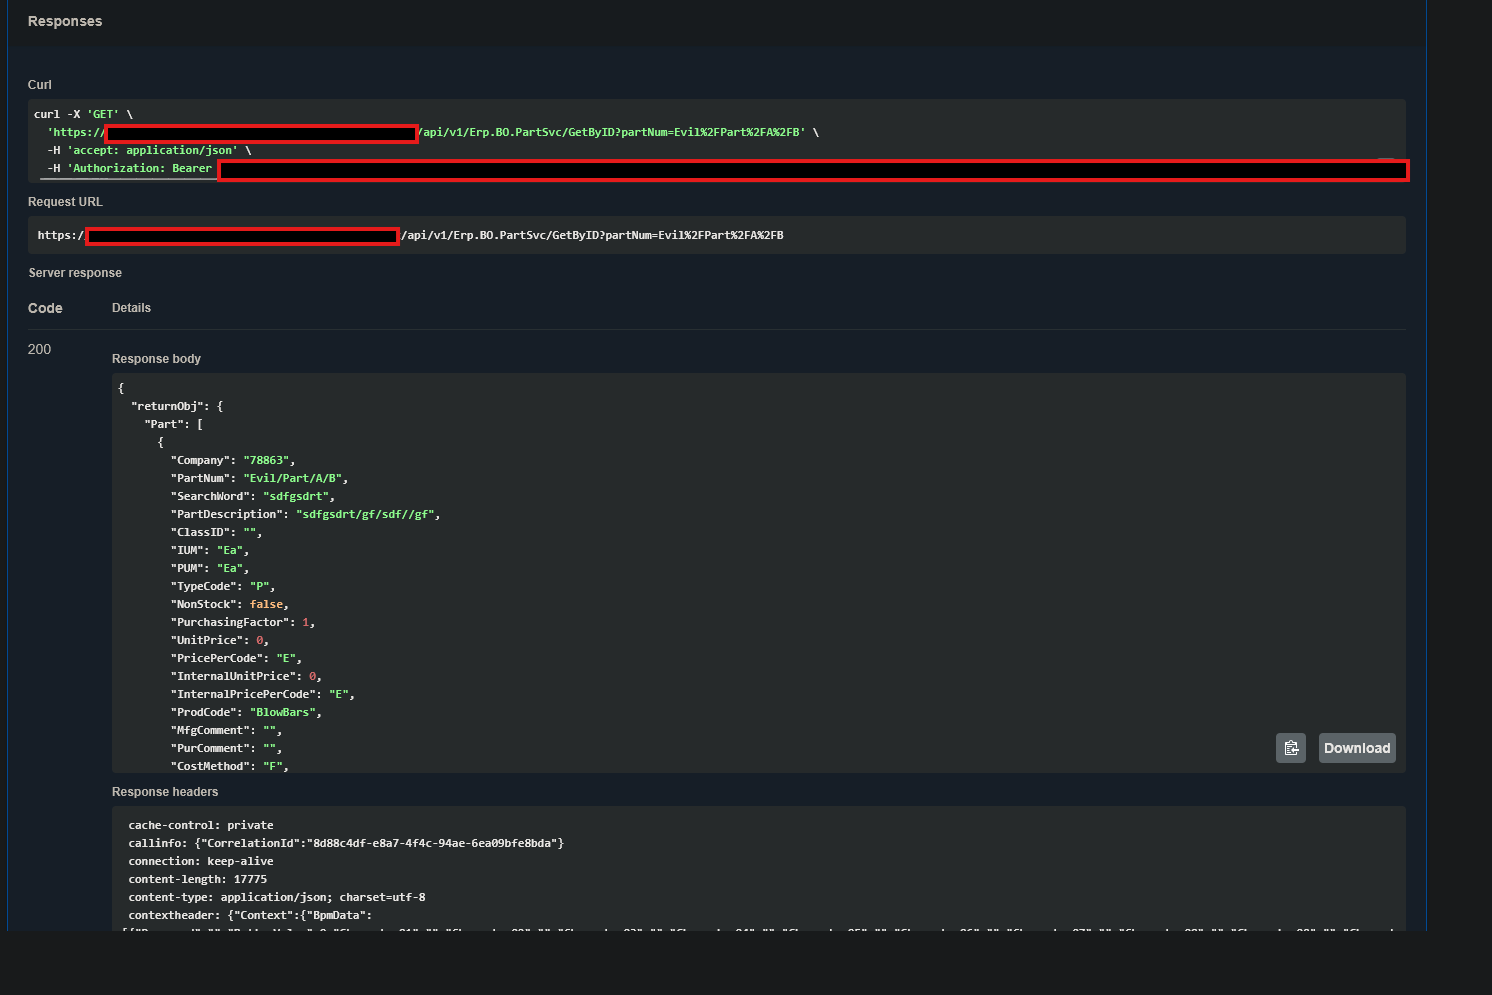
That’s not the same call I’m making. You’re calling GetByID. Try calling Erp.BO.PartSvc/Part(companyID, partNum). v1 or v2 doesn’t seem to matter.
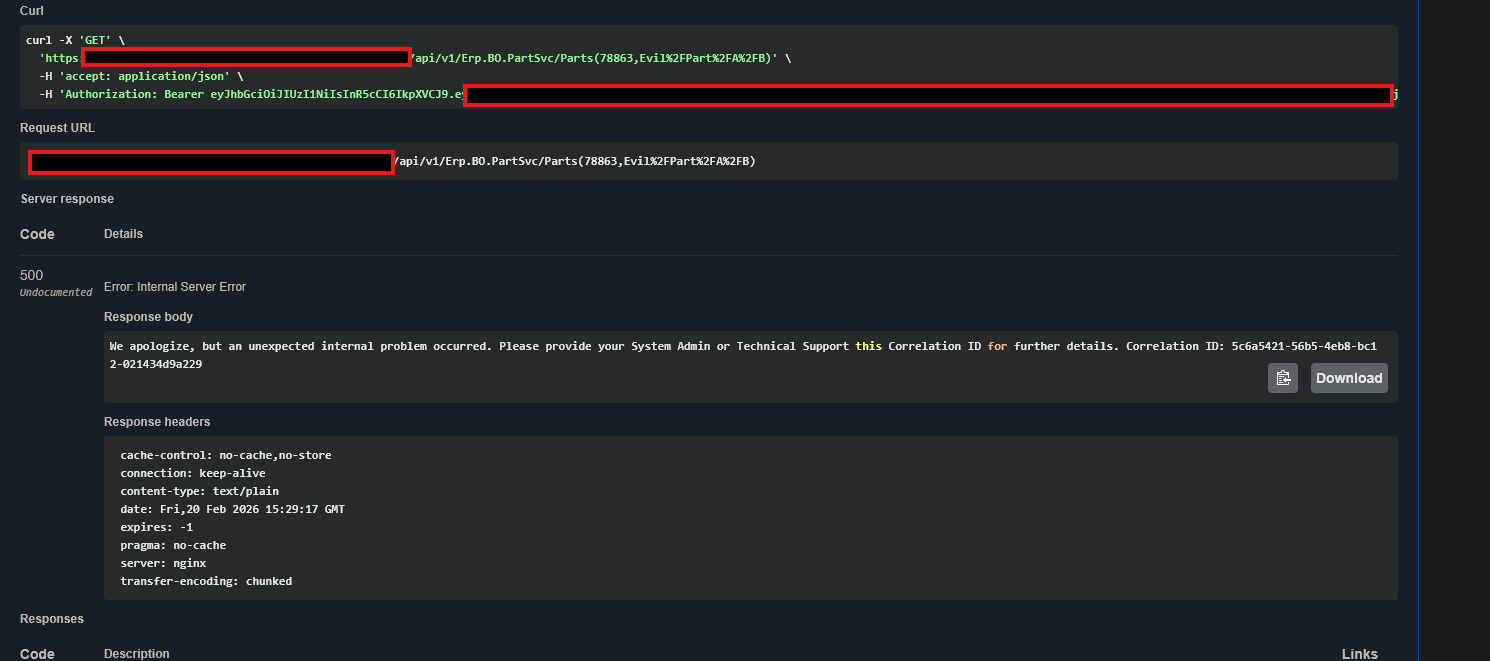
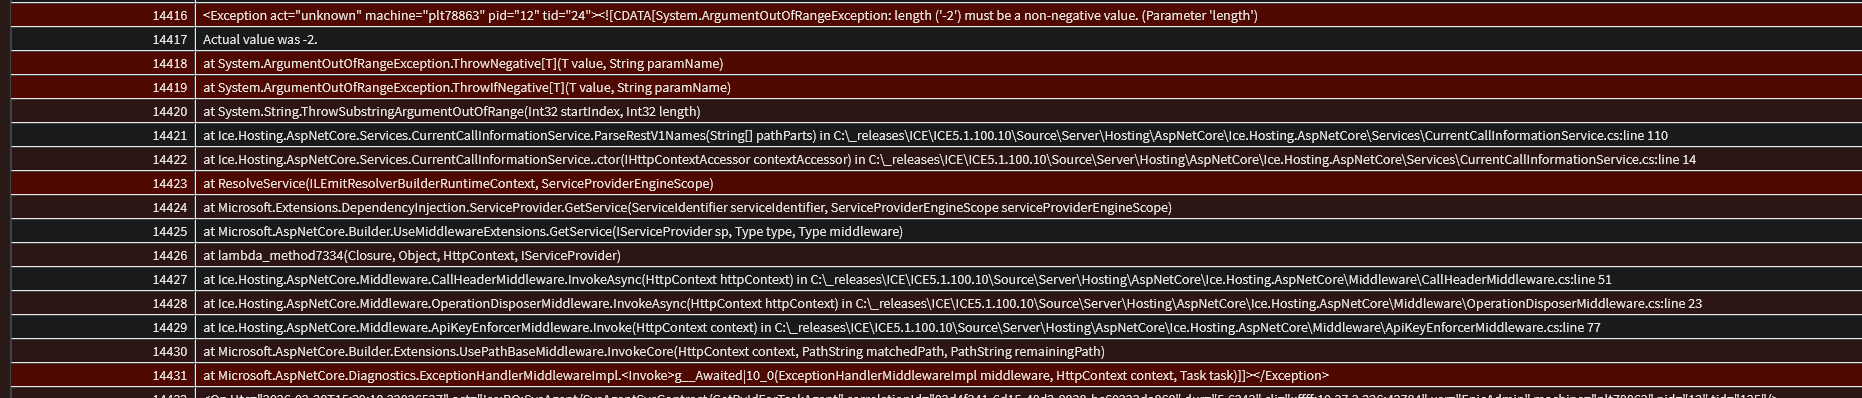
I’m on the same version in windows… I’m getting more and more suspecious of Linux
Can one of you post your RESPOSE headers from the calls. See if we can determine if Linux is being run through KESTREL or via reverse proxy?
 cache-control: no-cache,no-store
 connection: keep-alive
 content-type: text/plain
 date: Fri,20 Feb 2026 15:29:17 GMT
 expires: -1
 pragma: no-cache
 server: nginx
 transfer-encoding: chunked
Ah they are reverse proxying in NGINX… I have one of those… Stand by
OK!!! Now we’re getting somewhere. Thanks Evan!
@josecgomez there was an nginx update over this past weekend. What I don’t understand is how a web host update could foul up an API signature, unless the transfer from the proxy is somehow corrupting the data?
Well the NGINX proxy may not be properly handling URL encoding. Here’s what might be happening:
When a client sends a request with special characters (like spaces, parentheses, etc.) in the URL, those characters should be URL-encoded (%20 for space, %28 for “(”, etc.). The reverse proxy has to decide whether to:
- Pass the encoded URL as-is to the backend (Epicor)
- Decode and re-encode the URL before forwarding
- Normalize/sanitize the URL in some way
If NGINX is decoding the URL and then passing it to Epicor without proper re-encoding, or if it’s applying different encoding rules than what Epicor expects, you could end up with mismatches. This is especially problematic with characters that have special meaning in URLs or URIs.
There are specific NGINX directives that control this behavior:
proxy_passwith/without trailing slashes behaves differently- URL rewrite rules can inadvertently decode/re-encode
- The
$request_urivs$urivariables handle encoding differently
I have an NGINX proxy in front of my Epicor environment - I’m gonna test this there and see if there’s a specific config directive that needs to be adjusted to preserve the exact encoding that Epicor expects.
This makes sense, thank you!
What about NGINX Proxy? I’m trying to teest it but I forgot mine runs through IIS. I’m setting up a new test.
i don’t have it 